Perspective
Audit-Ready by Design
 Audit-Ready by Design
Compliance officers have questions about AI. Good ones. As financial institutions adopt AI tools, the compliance function faces a new and unfamiliar challenge: how do you audit decisions that were assisted by artificial intelligence? How do you demonstrate to regulators that proper controls were in place when the "decision-maker" was an algorithm?
These aren't hypothetical concerns. Regulators are actively developing frameworks for AI governance in financial services. The institutions that get this right will have a competitive advantage. Those that get it wrong will face enforcement actions, reputational damage, and operational disruptions.
We sat down with our product team to address the questions we hear most often from compliance officers, risk managers, and internal auditors evaluating AI platforms.
Q: How do I know what the AI actually did?
A: This is the foundational question, and Scalata's Knowledge Graph provides a complete answer. The system records everything: "Who asked, what it was understood to mean, which specialist took it, what it read, where the figures came from and what came back—written down as it happens, and drawn as a graph anyone in the room can follow."
Every answer has a story you can walk back, step by step. When an auditor asks "how did you arrive at this conclusion?", you can show them the exact path: the data sources consulted, the calculations performed, the logic applied. Nothing is hidden in a black box.
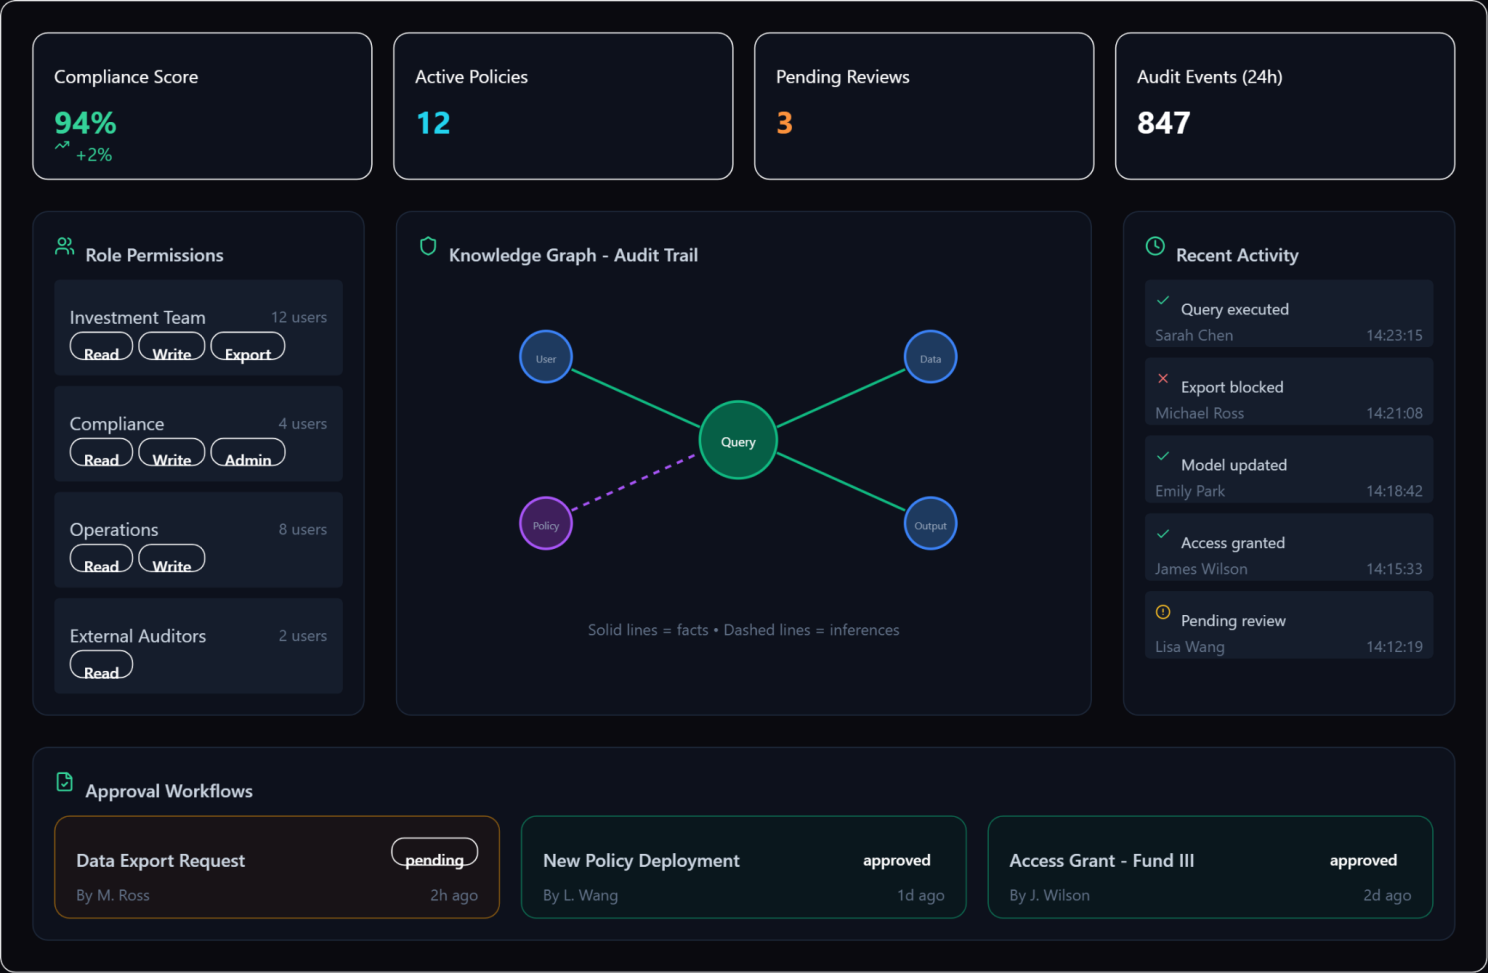 Knowledge Graph Audit Trail
Q: How do you distinguish between facts and AI-generated inferences?
A: This is a critical distinction that many AI systems blur. Scalata makes it explicit: "Two kinds of line are drawn: what happened, and what was inferred from it happening repeatedly. The second kind is dashed, always, so an inference is never mistaken for a fact."
When you're reviewing an output, you can immediately see which elements are direct observations from source data and which are patterns the system identified. This distinction matters enormously for compliance—a regulatory filing based on facts requires different validation than one based on inferences.
 Facts and AI-Generated Inferences
Q: Can different people have different access levels?
A: Absolutely. "Everyone can ask. Not everyone sees the same answer." The platform supports granular access controls that mirror your organizational structure.
The system provides three roles with four rights under each—create, read, update, delete—held per capability rather than as a single switch. Departments nest as deep as your organization actually does. Individual grants determine which surfaces a person sees, who they may share with, and whether anything may leave the building.
A junior analyst might be able to query portfolio data but not modify compliance rules. A compliance officer might have read access across all departments but write access only within their function. The controls are as granular as you need them to be.
 Granular Access Controls
Q: What about external users and guests?
A: External collaboration is common in finance—auditors, consultants, counterparties, regulators. Scalata handles this without compromising security: "Guests get permissions of their own rather than a hole in the wall."
External parties can access exactly what they need—nothing more—with full auditability of their interactions. You can grant an auditor access to specific data sets for a defined period, and the system will log every query they run.
Q: How do we enforce our internal policies?
A: Scalata's Compliance AI operates on a simple but powerful principle: "Nothing moves until it has passed your rules." You define the guardrails in your own words—plain language, not code—and the system enforces them automatically.
Every request and every answer is screened against your policies before it reaches a model, a colleague, or a client. Violations are blocked outright or sanitized as appropriate. You're not relying on users to remember the rules; the system enforces them.
Q: How do we know if our policies are working?
A: The platform produces a compliance score built from how much of the organization a policy reaches and how well what it catches holds up under review. Gaps are named explicitly—you can see which policies aren't being applied consistently and where violations are clustering.
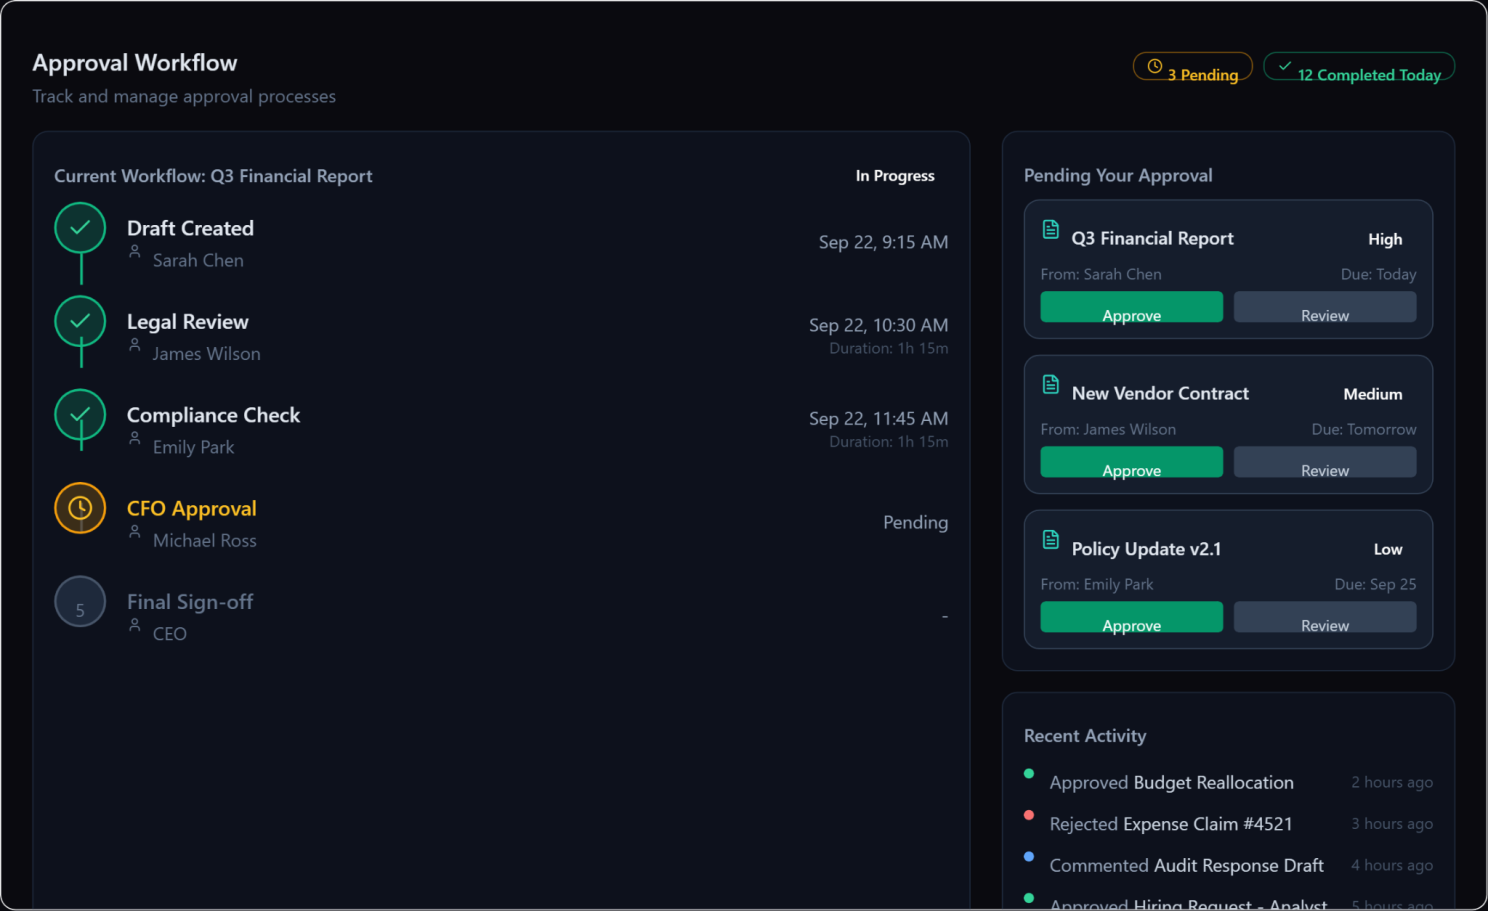
Events that require human judgment are queued for confirmation rather than auto-resolved. Reports are generated from the record, giving you audit-ready documentation of your compliance posture at any point in time.
 Compliance AI
Q: Can the AI make things up?
A: "Hallucination" is the industry term for AI systems generating plausible-sounding but false information. It's a legitimate concern, and Scalata addresses it directly. The platform is built on a core principle: "Every answer is cited and traceable. Anti-hallucination guardrails keep the analysis honest and defensible."
When the system provides an answer, it shows you where that answer came from. If it can't cite a source, it tells you. The Knowledge Graph's distinction between facts and inferences adds another layer of protection—you always know when you're looking at source data versus derived conclusions.
Q: What's the bottom line for compliance?
A: The bottom line is architectural: "Data governance and auditability are built in from the first line of code, not bolted on." Compliance isn't a feature added to satisfy regulators; it's fundamental to how the platform operates.
When the auditors arrive—and they will—the record will be waiting. Complete, accurate, and ready. Every administrative change documented. Every decision traceable. Every policy enforcement logged. That's what audit-ready by design actually means.